Skip to content

Quantum-safe cryptography 

Adversaries don’t need a quantum computer to start attacking your data. Encrypted traffic intercepted today can be stored cheaply and decrypted the day quantum computing matures. Regulations demand you start building your crypto inventory.

Powerful quantum-safe security solutions

Some data will outlive your encryption

If your data must stay confidential for ten years or more, the exposure to Harvest now, decrypt later (HNDL) attacks began the moment it crossed a network. Examples of such data include:

  • classified material
  • diplomatic correspondence
  • patient or medical records
  • intellectual property
  • financial transactions
  • OT telemetry, OT infrastructure details and login credentials

The systems that matter most can't be upgraded

Protected by default

Browsers, email, and cloud services are updated on a vendor's schedule in the background.

Exposed for years, possibly forever

Legacy applications and IT on proprietary protocols. OT and ICS with decades-long lifecycles. Embedded devices without the compute for post quantum algorithms. Third-party connections your organization doesn't control.

Square Image 10_DataCenter

The post-quantum cryptography (PQC) transition has deadlines

Across Europe, the United States and Asia-Pacific, governments and regulators have put dates on the move to quantum-safe world. Typically, the recommend post-quantum cryptography as the method. 

Europe

2026

National plans and crypto inventories

  • 2026Planning starts alongside with crypto inventories
  • 2030High-risk use cases migrated to PQC
  • 2035Medium-risk use cases

United States

2027

CNSA 2.0 for new security systems

  • 2027CNSA 2.0 for new security systems
  • 2030PQC key exchange, federal & defense
  • 2031PQC signatures

Asia-Pacific

2027

Singapore critical infrastructure plans due

  • 2027Singapore CII migration plans
  • 2030Australia retires classical crypto
  • 2035Japan government systems migrated

Sources: EU Coordinated PQC Roadmap; US EO 14412, NSA CNSA 2.0; Singapore CSA, Australian Signals Directorate, Japan NCO. Status November 2026; some milestones are guidance rather than law. Not legal advice.

Not sure where to get started? Download the PQC migration guide now.

Your first practical steps to becoming quantum-safe

1. Protect data in transit against harvest now, decrypt later 

Critical organizations have the obligation to protect long-lived data against present and future threats. The good news is your organization does not need a market-wide quantum-safe rollout or a finished standard to get going. You also don’t need a finished inventory to start. 

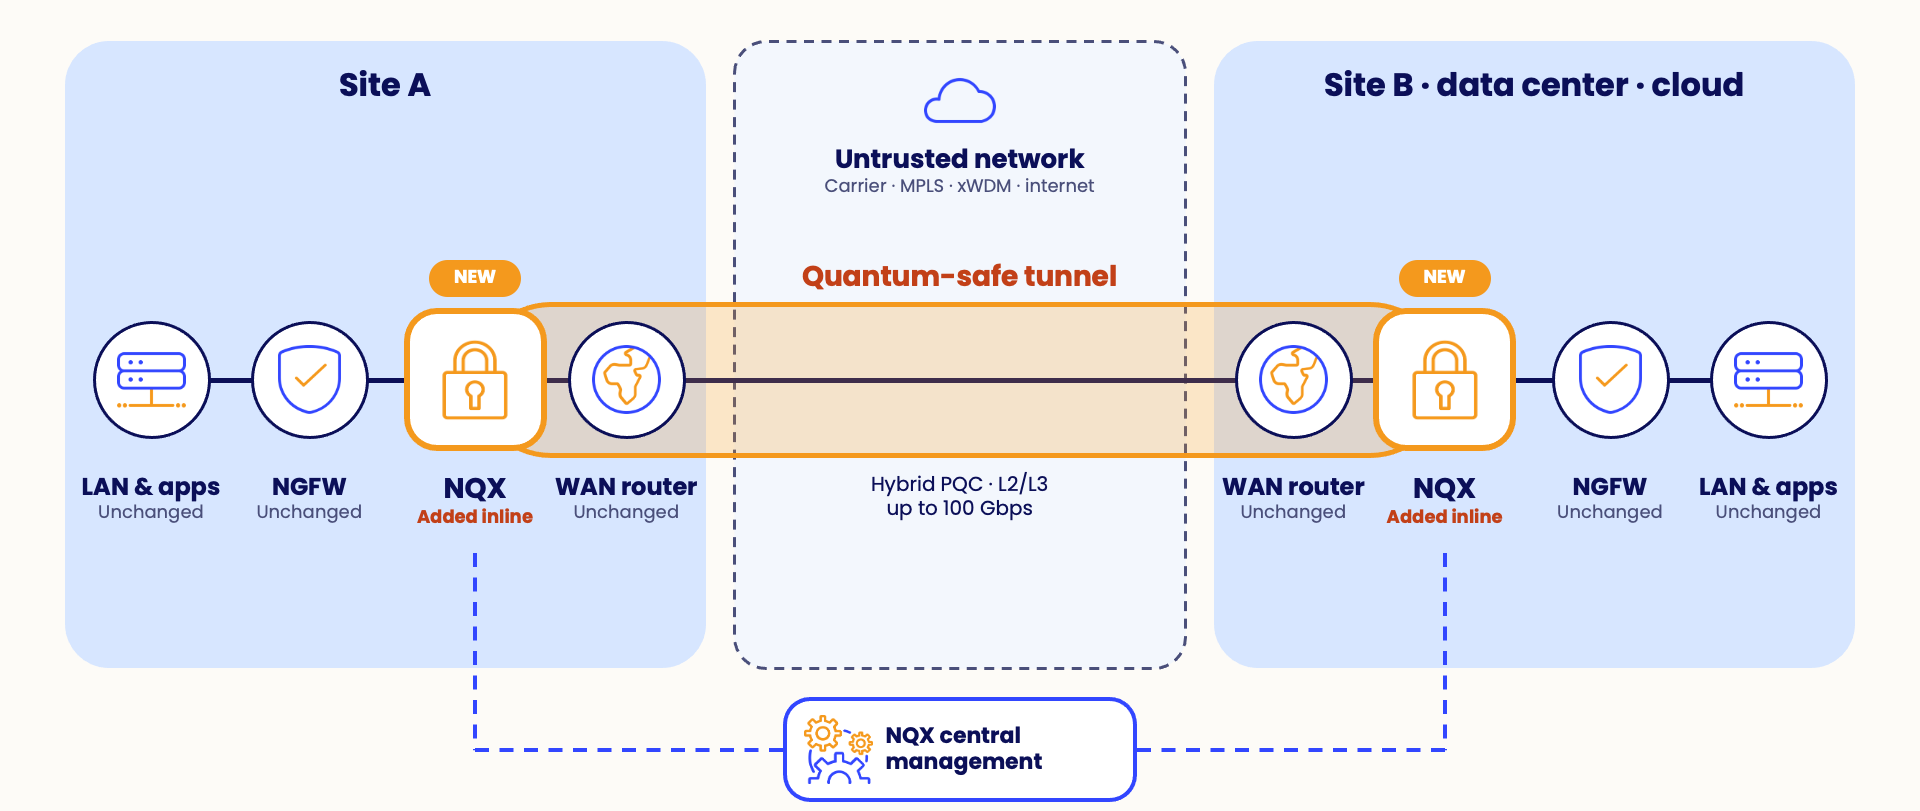
With quantum-safe network encryption, you build resiliency and protect data in transit against harvest now, decrypt later while building your inventory. With a network encryptor like NQX, you can:

embed any data traffic inside a quantum-safe overlay at the network level (L2/L3)

protect all traffic, starting from the network backbone all the way to the application layer

secure app-to-app, site-to-site, data center to data center connections over untrusted networks with a single solution

keep your infrastructure intact and quantum resilient

NQX_Overlay_Deployment-1-1

2. Start your discovery phase with an SSH crypto inventory

Creating a crypto inventory of your entire tech stack and Cryptographic Bill of Materials (CBOM) is a big task that might take years. Start your discovery phase with a Secure Shell inventory: Discover and inventory your SSH keys and cryptographic assets, assess their crypto-agility level, and understand where to prioritize your migration to PQC - with guidance from the inventors of SSH.


Learn more about quantum-safe migration


Quantum-1

Different approaches to quantum safety

Quantum computing poses different risks to different encryption methods. Explore our comparison page to understand your options and why choosing the right approach to quantum safe cryptography matters for your company. Compare different different approaches to become quantum safe. 

Network encryption complements firewalls and VPNs

Network encryption based on PQC complements your installed base. Learn more about how our NQX Network Encryptor offers high-throughput quantum resiliency while allowing firewalls and VPNs to do what they do best.

How NQX Network Encryptor complements firewalls and VPNs.

A pragmatic first 90 days

Square Image 1_DataCenter

01 Prioritize data in transit

It's where harvest-now-decrypt-later hits first, and where protection can be added without changing systems

02 Require crypto-agility

In anything you procure, so evolving standards never force a rip-and-replace upgrade.

03 Align with your mandate

EO deadlines, NIS2, DORA, ECB supervisory expectations — know which applies and what evidence you'll need to show.

04 Inventory

While protecting data in transit, build your inventory and Cryptographic Bill of Materials (CBOM).

05 Map exposure

Which sensitive data crosses which links, and how long must it stay confidential?

Square Image 1_DataCenter

Our quantum safe portfolio

For long-lived data in transit

NQX™

NQX™ is a TL III (EU Confidential) certified quantum-safe network encryptor that protects data in transit at Layer 2 (Ethernet) and Layer 3 (IP) at up to 100 Gbps line rate. This includes classified data.

For SSH discovery and inventory

PrivX™ Key Manager

Discovers all your SSH-related assets, creates your PQC crypto-inventory, and analyzes your crypto-agility level (also on asset level).

PrivX™ Insights

A service built to take inventory of your cryptographic SSH assets together with our experts.

For access management and TCP/mainframe connections

PrivX™ PAM 

Secures privileged human and non-human identity (NHI) access to critical targets with quantum-safe sessions.

Tectia® SSH Server

Transparent, quantum safe tunneling for TCP applications without changing the apps. 

Tectia® SSH Server for IBM z/OS 

Future-proofs your mainframe communications with Post-Quantum Cryptography (PQC) algorithms. 
Explore quantum security resources

Securing terrestrial satellite data

Securing terrestrial satellite data

Preparing for the Post-Quantum Era: A Guide to Quantum-Safe Migration

Preparing for the Post-Quantum Era: A Guide to Quantum-Safe Migration

Frequently Asked Questions

Quantum-safe migration FAQ

What if a quantum-safe program feels too big to start?

Focus. Wrap your data in transit inside a PQC tunnel while you take an inventory of your long-lived, high-value data.


Isn’t quantum a future problem?
What if we choose the wrong algorithm?
Isn’t migration to quantum safe environments slow and expensive since it requires changing configurations, apps and hardware?
How much will PQC slow our network down?
Is there a risk we lose control and sovereignty?

Get a jump start on your quantum safe journey now.